New Feature: JupiterOne Compliance Dashboard
Track Compliance in Real-Time
Security Assurance never looked so good.
Security analysts and teams face a tall task when it comes to deploying new resources, team members and devices at scale while still being expected to maintain secure operations. The number of changes occurring at any time ripples to areas throughout the organization, making keeping an up to date view of what is going on in your environment difficult to say the least.
JupiterOne tackled this challenge head on with its asset inventory, which fetches and classifies entities in your environment automatically, and the ability to search across your environment. This proactive management is helpful when you are investigating changes, but the burden of compliance audits and self-assessments can still be overwhelming.
Making Compliance Status Easy to Track
We are excited to announce JupiterOne's latest feature: the Compliance Dashboard.
After laying the groundwork for efficient management of your security operations by bringing in data constantly to stay up to date with changes and plotting these resources and entities against security policies and procedures with the policy builder, security analysts and teams are now able to view their active compliance status against any controls or requirements. Teams can import any security or compliance framework their organization is aligning with.
Walking Through the Compliance Dashboard
A Complete View

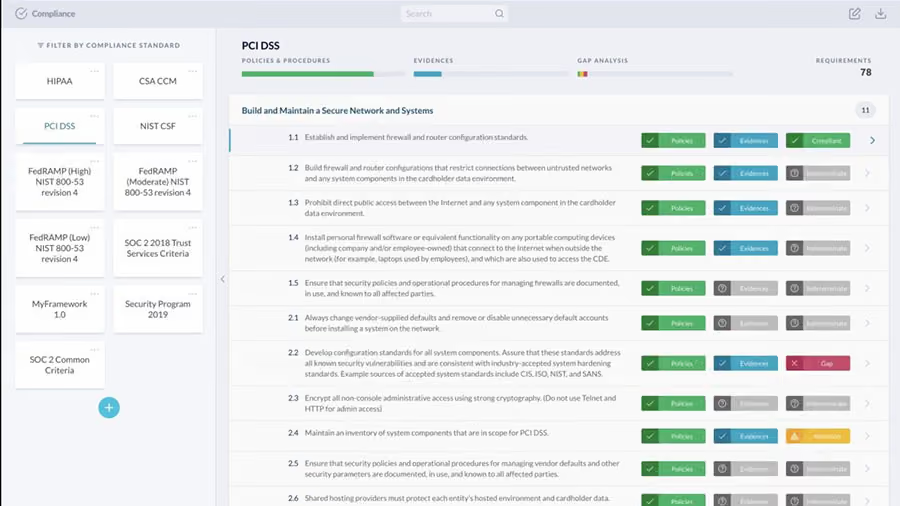
JupiterOne's Compliance dashboard starts at the highest level, providing an overview of top level controls or policies making up a security framework. For example, an organization wanting to get a sense for how they stand in terms of adopting CIS Control can select the security framework to see the 20 Basic, Foundational and Organizational Security Controls.
From Controls to the Requirements that Make Up the Control

From the Controls, teams can dig into the specific requirements. This is where security analysts and teams can easily spot where they are in compliance (green), out of compliance (red – coming soon) or if evidence wasn't found (yellow). It's a quick glance to get a gauge of your security operations health.